Apache Superset Customization & Keycloak SSO
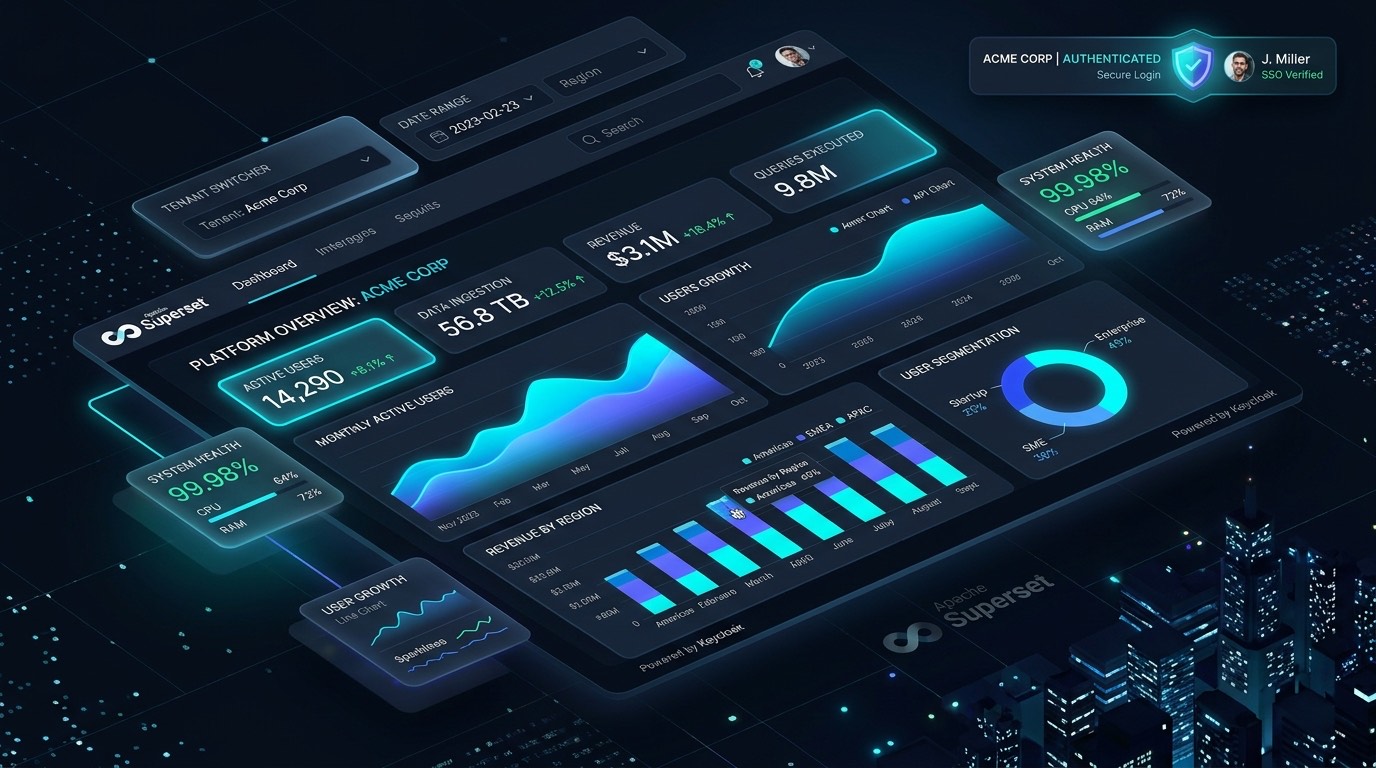
Customized Apache Superset with Keycloak OAuth2 SSO and secure multi-tenant embedded analytics.
Operational & Architectural Constraints
A B2B SaaS platform wanted to provide interactive analytical reporting to enterprise clients without building charts and filters from scratch. However, the default Apache Superset distribution lacked native integration with their central Keycloak identity provider, and standard embedding risked exposing one tenant's raw datasets to another without strict row-level isolation.
System Design & Implementation
We engineered a custom Apache Superset deployment. We extended Flask-AppBuilder's security manager with a custom Python authentication module that validates Keycloak OIDC tokens and automatically maps Keycloak realm roles to granular Superset permissions. For customer-facing embedding, we implemented a backend endpoint issuing scoped guest tokens containing dynamic Row-Level Security (RLS) rules, enabling secure iframe embedding within the SaaS React application.
End-to-End System Data Flow
System Data Flow: Apache Superset Customization & Keycloak SSO
Internal staff authenticate via Keycloak SSO; external SaaS users receive cryptographically signed guest tokens with RLS constraints directly restricting query results.
Requests an ephemeral dashboard session from the application backend for an authenticated tenant user.
Strict tenant isolation and atomic data boundaries enforced at both gateway validation and persistence/table tiers.
Every stage emits structured trace contexts (OpenTelemetry / correlation IDs) for distributed debugging and latency profiling.
Key Engineering Decisions
Ephemeral guest tokens with RLS over separate Superset user accounts
Eliminated the overhead of synchronizing thousands of external SaaS end-users into the Superset database.
Requires backend server-to-server call to generate tokens before dashboard render.
Redis caching for analytical dashboard queries
Cached identical dashboard slices across concurrent tenant users, drastically reducing direct warehouse load.
Requires fine-tuned cache invalidation policies (TTL configured to 1 hour).
Measured System Results & Stability Guarantees
In accordance with our engineering verification policy, we document verified technical benchmarks and architectural milestones rather than unverifiable marketing claims.
Analytics & Business Intelligence
Explore our full deliverables, tech stack, and engagement models for this capability.
Facing a Similar Engineering Challenge?
Whether you need to decouple a monolith, deploy an Azure Databricks Medallion lakehouse, or author custom Airbyte connectors, let's evaluate your technical requirements.