Enterprise Multi-Tenant Microservices Platform
Engineered a high-availability, tenant-isolated microservices architecture with centralized Keycloak SSO.
Operational & Architectural Constraints
A growing enterprise software platform needed to transition from an overburdened monolithic codebase to a modular architecture capable of serving multiple independent business tenants. The existing system suffered from high blast radius on deploys, lack of granular tenant data isolation, and fragmented authentication logic duplicated across legacy endpoints.
System Design & Implementation
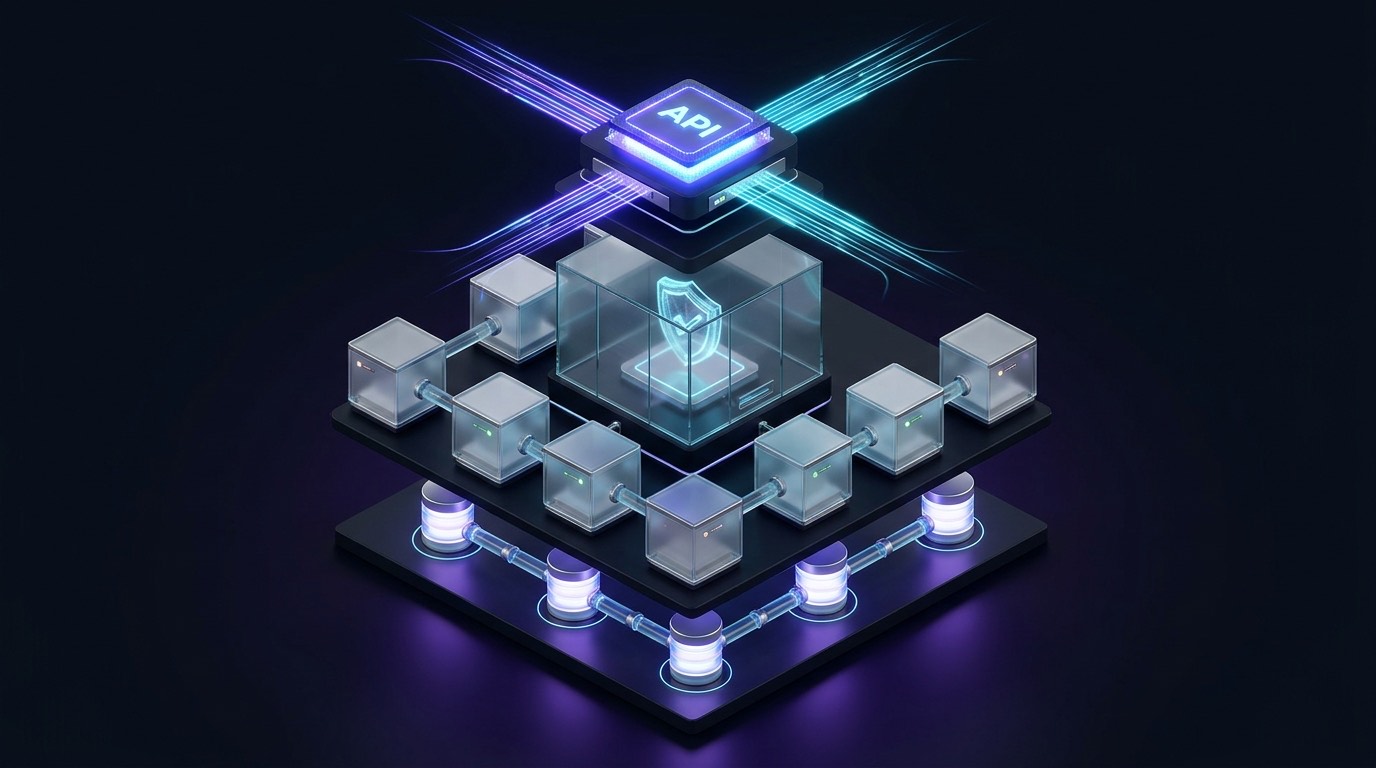
We architected a distributed microservices ecosystem using Java 17 and Spring Boot 3.x, deployed on Kubernetes. A centralized Keycloak instance was established to handle identity federation, OIDC token issuance, and tenant-scoped role-based access control (RBAC). Data isolation was implemented at the database layer using tenant schema discrimination and tenant-aware connection routing, preventing cross-tenant data leakage while sharing pooled compute infrastructure.
Terminates TLS, checks Keycloak RS256 token validity, extracts tenant claims, and injects tenant-context header.
Stateless pods reading TenantContextThreadLocal to route operations dynamically without shared memory leakage.
Dynamic DataSource router points queries to distinct PostgreSQL schemas per tenant organization.
End-to-End System Data Flow
System Data Flow: Enterprise Multi-Tenant Microservices Platform
Client requests terminate at the API Gateway, which validates Keycloak JWTs and extracts tenant context before forwarding to downstream microservices with encrypted context headers.
Performs TLS termination, rate-limiting per tenant API key, and JWT signature verification against Keycloak JWKS endpoints.
Strict tenant isolation and atomic data boundaries enforced at both gateway validation and persistence/table tiers.
Every stage emits structured trace contexts (OpenTelemetry / correlation IDs) for distributed debugging and latency profiling.
Key Engineering Decisions
Schema-per-tenant isolation over shared table discriminator column
Ensures complete data segregation, simplified tenant backups, and regulatory compliance without risking SQL filter omission bugs.
Requires automated database migration scripts that iterate across all active tenant schemas during releases.
Stateless JWT validation via cached JWKS keys
Eliminated the need for microservices to perform network calls back to the identity provider on every single API request.
Token revocation requires short TTL (15 mins) paired with refresh token rotation flows.
Measured System Results & Stability Guarantees
In accordance with our engineering verification policy, we document verified technical benchmarks and architectural milestones rather than unverifiable marketing claims.
Backend Engineering & Distributed Systems
Explore our full deliverables, tech stack, and engagement models for this capability.
Facing a Similar Engineering Challenge?
Whether you need to decouple a monolith, deploy an Azure Databricks Medallion lakehouse, or author custom Airbyte connectors, let's evaluate your technical requirements.